Showing posts with label Events. Show all posts

Wednesday, 21 November 2012

Owning the flag: PoliCTF

We like to imagine the good ol' days of princesses and dragons, where the heroes sat around a smoky tavern waiting for quests from frail old wizards. These days, the heroes of our time sit around computers getting their quests from a server on the Internet. That was how our weekend went...


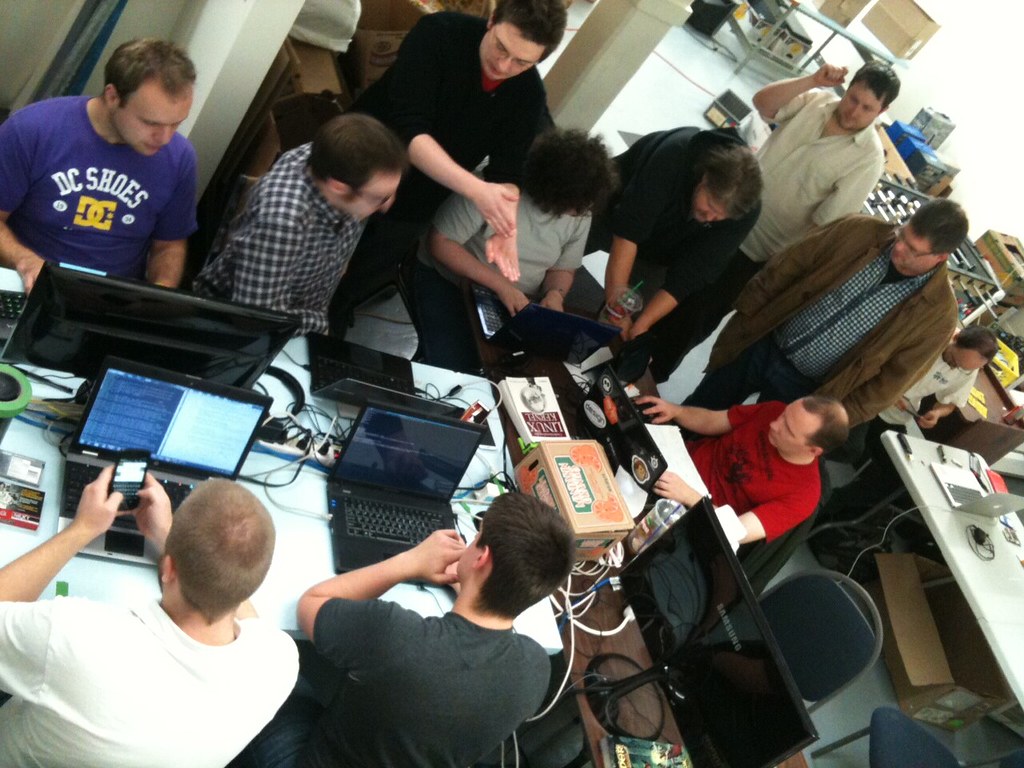
An eager group of us met up Saturday at 1 pm — Alex, Colin, Jay, Jeremy, Mak, Richard, and I (Ron). Armed with junk food and piles of computer gear, we set out on our quest: to capture all the flags!

The clock ticked. It hit 1:00. Nothing yet. 1:01, 1:02, and finally at 1:03 the first challenges were up! Mak started decrypting them while the rest of us waited. Slowly, we started getting the puzzles. A PCAP of a SSH session for Forensics, a C program that said "U MAD?" for Bin-Pwn, a bunch of encrypted data for Crypto, and an obscure Hackers reference for Grab-Bag.

An hour of derping later, and all we could wonder is what we had gotten ourselves into. As we were working, other teams were completing challenges, and we were falling behind. What's going on? Are we that derpy!? New challenges were unlocking — a bitmap with faded text for Forensics, a network service for Bin-Pwn that was a calculator, and a photo of a crazy breadboard for Grab-Bag. And there we sat, still derping.

Grab-Bag 100: Hackers


Eventually, Richard realized that the obscure Hackers reference meant we had to watch the movie and find the scene where they showed the Garbage File. So he and Mak fired up Netflix, and spent a half-hour jumping around looking for the two frames in which the hex dump of the file showed the address we needed. First flag: DEFEATED! 100 points! w00t! High fives all around!

Things were looking good! Let's get our hopes up so we can really feel it good when we fail!

Forensics 100: Beep beeeeeep beep


Next up, the SSH session. After a bunch of screwing around looking for any kind of data leakage, we started looking at the SSH traffic. Nothing jumped out, and we didn't even have the handshake so we didn't know how it was encrypted. WAT DO?

Eventually, the challenge coordinators released a hint: "This challenge could just as easily be RSH". Wait, what? SSH is encrypted, RSH is not. Hmm! That led me to start thinking of covert channels. We started looking at the packets' metadata, but didn't see anything interesting. Alex points out that there are large and odd gaps in the ssh traffic, like eight second gaps once in awhile. We opened a timing graph, and I said, "This is modulated.", and we were right. A horrified look crossed Mak's face as we all came to the realization: it's Morse code. With SSH packets. Wow.

So, we decoded it, and sure enough, it was a flag. FLAG 2! There was much rejoicing, and the best high five I've ever had with Mak. I swear we were breaking atomic bonds between our hands... [Editor's Note: I still have flashbacks and phantom pains as a result.]

By that time, it was 8 or 9 pm. We were in the middle of the pack and going strong. But I'm not gonna lie, the rest of the night/morning is a bit of a blur, fuelled by junk food and sugar, so I'm just going to hit on the high points, to the best of my recollection, in vaguely chronological order.

Bin-Pwn 300: Please don't ask me about Bin-Pwn 300


Bin-Pwn 300. Oh God, Bin-Pwn 300. It was a Linux binary that was running on their server. It became quickly obvious that you had to exploit it, but despite reversing the whole damn thing, I couldn't find the issue. I'm supposed to be good at that stuff! Sadly, I'm not so good at Linux debugging/hacking, so it slipped through the cracks despite spending all night on it. Sadfaec. :(

Luckily, I'm not the only one with a nemesis! Forensics 200. You can see the look of horror on Mak's face just by mentioning it. When I brought it up in the SkullSpace meeting, he publicly threatened to stab me in the face. It's just that good!

Forensics 200: Please ask Mak about Forensics 200

Forensics 200 was a BMP image.


The hint noted "This file is big 54 + PixelArraySize." That's it. We already knew from the previous level, the Morse code, that there would be something hidden in some insane manner. Looking closely, we could see that there was some text somewhat superimposed on the image. Mak wrote a Ruby script that would take the original BMP as input and output a directory full of mangled BMPs with the same pixel data, but with a different height and width declared. Alex ran the script and eventually identified the text as "BITCHES BITCHES EVERYWHERE". Surprisingly quickly, Mak, in the supercomputer he calls a brain, realized that the bytes were encoded funny, and that there was likely some stenography on the pixel data in there, causing the strange colouring. He threw together another Ruby script, and before long had pulled out the least-significant nibble (4-bit value) from each byte of pixel data to form a new file. And guess what? IT WAS ANOTHER IMAGE!

That image, Mak eventually realized after some nudging from Mark, had extra data after the pixel data. It was a 7zip archive! By midnight, we had the 7zip archive. By 1pm the next day, we still had the 7zip archive. It turns out, the password was stego-encoded in the second BMP in a way that we never did figure out. We still don't understand it now that another team has explained it to us. It was a sad time...

At some point pizza showed up. I don't eat pizza, but I also had a box of oranges, triscuits, bunny-shaped graham crackers, chips, dip, guacamole, bagels, ... well, let's just say I had a lot of food. Also a couple bottles of Kambucha. I love that stuff!

Anyway, on to other flags. Did I mention I worked on Bin-Pwn 300 all night? I'm still upset with that.

Bin-Pwn 100: U MAD?

Other flags... oh yeah, Bin-Pwn 100. Jay, poor Jay, spent far too much time chasing a white rabbit on that one. See, they had a weird combination of whitespace in each line: tabs and spaces. We tried all sorts of stego techniques, but no luck.

Let me back up. The level was a simple .c file that used a copy of libjpeg.a to generate an image saying "U MAD?" — the answer was, of course, "Yes, fuck off." At least, it was by the end of the night.

So anyway, Jay was playing with the whitespace in various ways and getting nowhere. He also tried to compile it against a system version of libjpeg.a and hash the output images... they were identical. So no hidden features in libjpeg.a. WAT DO?

That's when Alex took a look. Or maybe it was later, things are kinda hazy. Alex opened up libjpeg.a as an archive (and that night, I learned that .a files are just collections of .o files  — who knew?) and discovered a .jpeg file embedded. That's not right! The jpeg file, however, had a corrupted header. But, once he took the header from the original "U MAD?" .jpeg file and stuck it on the new one, it displayed a key above the text. We no longer mad, bro!

At some point that night, Ian and Marcella showed up and took some pictures. They are here. It was cool to see some friendly faces in the middle of the night. Actually, a lot of people stopped by here and there to help and cheer us on.

Bin-Pwn 200: 1 + 1 = 2

Bin-Pwn 200 was, basically, a calculator. You netcat to their server on a given port and it lets you enter two numbers and an operator. Those values are combined and the result is printed. That's it. What the fuzzle!?

This is where Jay saved us. He discovered that whitespace was handled wrong. If you added spaces, multiple numbers were used. For example, "1 1 1", "+", "2 2" would wind up as "7". How do? He quickly realized that he was looking at a Lisp-based evaluator. At that point, he had to leave.

Mak and Nick, a remote teammate, took over and started looking at this puzzle. They eventually figured out which Lisp dialect it is, and used these things they called "lambdas" to do all the magic: listing files, reading them, etc. With that, they managed to read "flag.txt" in the calculator's working directory and get the flag. BOOM!

I remember the sun coming up. Sunday was a beautiful day, I think. I pulled my car around without putting on a jacket. The sun felt nice after 24 hours in a chair...

Bin-Pwn 400: Hutlh ghItlh pIqaD

If we couldn't get Bin-Pwn 300, how the heck were we supposed to get Bin-Pwn 400!? Who knows, but we tried anyway!

Once again, we were given a server and a port. But this time, we also had a username. The server was called "alien-server" or something. It was a SSH server, and we didn't have a password. Okay... so we need to break SSH? LAME!

After poking around a bit, Alex remembered that he had to send a SSH public key to the organizers to register our team for the contest. Aha! Sure enough, we logged in, expecting a shell. As the famous Chuck Testa would say, nope!

We logged in, and the server starts saying weird things. It starts by saying "loS", then waiting ten seconds, followed by other gibberish. I love me some ciphers, so I thought this might be fun! For fun, Alex Googled one of the phrases. We found an English-Klingon dictionary. Yup, it's Klingon. We bashed our heads trying to figure out what to type, but all it would respond with is "bad message" or something.

Nick discovered that the Klingon letter 'ch' could be used to read a file. But only a couple files were available, specifically, the files that were the source of the shell itself.

Once we had access to the files, Nick and I started working on how to exploit the system. Eventually we realized that we could get the system to interpret (or JIT compile, more likely) arbitrary C++ code by using a bunch of weird Klingon commands. I managed to write a file-reader to read flag.txt, and boom! We had another flag! I woke up Mak to high five him. It was a good time.

Shortly after that, I realized I couldn't stay vertical anymore so I laid down. I remember the voices fading out, the coldness, and then waking up with an arm covered in drool. An hour or two of sleep will do that. I woke up to cheering and high fives...

Grab-Bag 300: Duckrolled

I, probably fortunately, slept through this level. It was JavaScript code that, through a combination of nested packing, syntax errors, obfuscation, and duckrolling — was very annoying to decode.

Here's how I understand it happening: I went to sleep, Mark and Mak starting typing and pointing excitedly at the screen, then I was being woken up for high fives. It was a great level, at least for me. I wish they'd solve more like that. [Editor's Note: I wish you'd snore less. (-:|3]

By the time I woke up, I realized I was mostly useless and instead of continuing to bash my head, I started cleaning up and taking out the garbage. That way, when the clock ran out, I could go straight home and get some more, much needed, sleep...

Grab-Bag 200: Blinkenlights

Now, if there's one thing I don't know — and believe me, there are a ton of one things I don't know — it's circuit diagrams. And, worse yet, pictures of breadboards with unknown ICs.

Once this level unlocked, we had a bunch of people looking at it. Andrew, Ben, Justin, Richard, and more. There were LEDs and wires and chips and resisters and stuff, and they had to figure out which LEDs would go on, I assume. What else do LEDs do, really?

After a couple hints from the organizers, including an extra image of the contraption from a new angle so that the wiring was actually visible, and working on it for the entire night, Richard figured it out, and we captured our sixth flag. This put us into tenth place overall, but unfortunately we lost a position in the last forty-five minutes of the contest.

And that's a wrap!

And that was the end. Six flags, eleventh place, and maybe six hours of sleep between the four of us who stayed the night (Alex, Mak, Richard, and I). It was intense!

Personally, I had a great time, and based on feedback from the others, so did they. As I said, we derped the hell outta the contest, but considering we got eleventh place with only four consistently present members on our team, that's darn good.

If I did it again, what would I do differently?
  • I'd get more sleep. I realize I burnt myself out. I bet I could have done better with a proper sleep.
  • Next, I'd try to get together a bigger group, and sleep/work in shifts.
  • I'd also like more space to work, and scratch paper.
  • I'd also like to suck less at debugging Linux applications.
All in all, though, I'm really happy with how it went. I approve!

If you're interested in helping out with other CTF challenges, email me, ron at skullsecurity.net, and let me know! I'll add you to our mailing list and we'll let you know when we plan to do our next time.

Monday, 7 November 2011

Hacking’s our business.

And business is good. The grand opening went better than anyone could have expected! After all was said and done, we took in over 800 dollars in profit! There was record attendance, and the (now finished) space was full of makers, hackers, geeks and self-professed nerds.

There were a whole bunch of projects on display ranging from arduino based thermometers, Lego NXT kits, steampunk nerf guns to hacked up television sets. As with other gatherings, we had a lockpicking island set up, complete with a visual guide to lockpicking for those willing to learn.
NXT kit and o-scope
Nuka Cola
lockpicking

For those willing and brave enough, there was the option of riding a homebuilt hovercraft! Though it doesn’t have a built-in mode of propulsion, we managed to come up with a way to move it by pulling the rider along using the extension cord. If you haven’t signed the waiver yet, make sure you do before taking a ride!

Molly and her hovercraft

Possibly because of the energy and excitement (and possibly because of the industrial-sized vat of coffee), conversations and project ideas were exchanged freely. I know that I picked up a whole bunch of new ideas, and as usual got to tap into the almost limitless knowledge found at SkullSpace. I can finish up a whole bunch of stuff I’ve been working on…and start on new projects I really don’t have the time and money for. But that seemed to be the general consensus in the space.

I managed to see Legary’s talk about vintage arcade machines and their security systems, and I have to admit it was riveting the whole way through. I didn’t think it was possible to learn that much about arcade machines in such a short span of time.

Speaking of arcade machines, both pinball machines were working, and as usual there was hardly a moment they weren’t being used. There’s nothing like hitting a big steel ball against electromechanical obstacles while the face of William Shatner stares back at you:
pinball!


Someone brought down an NES, and we played a bunch of classic games including Tetris and everyone’s favourite platformer – Spiritual Warfare. For those select few of you unfamiliar with the title, it’s a Christian adventure game where you find various pieces of God’s armour, use doves as currency and bring holy justice upon unsuspecting minorities.
Tetris!


I’m not sure how the game ends, exactly, but I can only assume it’s the rapture. After the meeting we all went down to the King’s head and redeemed our entry tickets for a free beer! It was icing on the cake. Not only did we get to hang out at a renovated and bustling SkullSpace, but we got a free fine brew out of the deal. DJ symbiotix provided the freshest, fastest beats while we continued our conversations. There was a lot to talk about - a whole lot of ideas to share and angles to gain on new projects.

If we can get this kind of turnout at the next hackathon, who knows what we’ll be able to get done!
Nerf guns and Tron bags!
hacked CRT

Tuesday, 29 March 2011

Back at the Lo

As you've probably figured out by the title, this week’s meeting was at the Lo pub. As usual it was good times, and we had a few new members show up! I'm still surprised seeing so many tech savvy people in Winnipeg, it’s one of those things you almost wouldn’t expect. We only had a few things to go over because we went over the details of finding a space in last week’s meeting.

For those of you who haven’t read the discussion emails, Jay is spearheading the RSSF, and has found two possible locations. The first is on 111 Lombard, and we’d be able to rent it on a monthly basis. There is of course a catch. There are planned renovations for the space, and at any given moment we could be kicked out. Though a little risky, the price is right, and for a trial space it may just fit the bill. Jay mentioned some issues with cleanliness, but I think a weekend spent with brooms, mops and buckets could go a long way.

The second space is at 250 McDermot and is an open area of 750sq ft. The price is $875, it requires a yearly contract, and is supposed to be in much better shape. If utilities are included in this price the space would be a prime candidate. The RSSF will investigate tomorrow and update us via email. If anyone wants to help Jay with calling agents, it’d be greatly appreciated. It doesn’t take long, and Jay will hook you up with all the info! Send an email to the discuss list!

That’s about all we have for spaces right now, if we can get more people calling and talking to agents our options will likely expand. There are a lot of spaces, but apparently none of the agents responsible for them answer the phone.

In other news, we’re planning ahead for our April hackathon, which will probably be on Saturday the 16th. Ron’s going to send out a survey asking about what you liked/disliked about the previous event and how we could improve. We’ve already learned a lot from our last hackathon, and this one is shaping up to be even better. We’re going to get more tables and chairs to create more of a workspace type feel, better separate the music and talk areas, and try to set up workshops where attendees can tinker and code socially. Also, we’re working on fixing the network issues.

We’re probably going to be focusing on embedded systems this time around, with talks potentially covering the Launchpad platform and more about the Arduino. We’d like to set up an arduino workshop and give a talk covering some aspect, then allow people to try it out on their own. The topic will probably be serial communication, as that’s not only easy to implement on the Arduino, it’s also applicable to other embedded platforms. I’ll be sending out an email!

ARDUINO LINKS!

If you haven’t gotten an arduino yet, here are some websites where you can score one! We highly suggest you get one and bring it to the hackathon.
Best bang for your buck is probably the budget pack

If you have a bit of extra cash to blow, the experimenter pack will get you set up with everything you need to learn about micros. I really wish this was around when I got my arduino

At the talk I mentioned a shortcoming of the platform was the lack of ports. They fixed the fuck out of that problem with the Arduino Mega

Check out the rest of Adafruit’s arduino stuff here.

If for some reason you’re not down for ordering from Adafruit, Makezine carries them.

So does Sparkfun

And Evil Mad Scientist sells a totally badass variant, the Diavolino

They stock all sorts of really cool stuff too, usually more one-off and hard to find than sparkfun.

Monday, 21 March 2011

Hackathon 4 was a huge success!

GREAT SUCCESS
Massive props to the record number of people who showed up! We hacked, picked locks, played with microcontrollers and met a whole bunch of really cool people. Oh, and we learned stuff. Apart from the formal talks, everyone there seemed to have information to share on one subject or another. Personally, I walked out of the meeting knowing more about coding, microcontrollers, digital security and copyright protection, and I’m sure the feeling extends to most everyone in attendance.

hacking
lockpicking
dropping beats

As you’ll note in the pictures, the event took place at the Nutty Club, home of Les.net. Les was kind enough to let us use his awesome ISP room to host our event. Not only did the place look really cool, it was located in the heart of downtown! Watching trains go by from the windows was pretty sweet too.

Les has all sorts of cool RC stuff, but I couldn't find any pictures. Just imagine the stool is Quadracopter or an awesome RC car:
rc stool

The Goldeneye tourney was some retro fun, though the game doesn’t seem to have aged all that well. The pixels were the size of our heads! It seems the single-joystick control also took some getting used to, and to think that we used to be impressed… But I digress.
goldeneye
Ron pwning n00bs:
n64 ron


Mark’s combination talk and challenge was really interesting. He discussed vulnerabilities in Plone web software. It was my first time watching hackers do their thing in real life, and though I didn't quite get what was going on I'm sure I absorbed some of the information by osmosis. Mark led us through the issues in Plone, and offered a prize for whoever could exploit it over the course of his talk. Stef ended up winning the challenge and took home an energy drink! Here's a skullspace simulation of the talk, reconstructed from photographs:
huzzah!

I covered some basics in Arduino, for anyone interested I have the powerpoint, so just send an email to the discuss list. I learned there's a few other people involved with skullspace that are into microcontrollers, which was really cool. I'd love to hear what you guys have to say about the Launchpad, as it's a system that I'm not at all familiar with but it looked really cool! I know I talked to two people, but since I'm terrible with names I've already forgotten...you know who you are though. If you guys would like to give a talk about micros or the launchpad at the next hackathon that'd be wicked!

Here's me, not talking about the arduino:
arduino talk

The talk I enjoyed most was FuckYeahNouns, skullspace’s most profitable project to date. Burke led us through the process of creating the site, as well as some awesome statistics from the moments the website was posted to Reddit. As a result of the talk, I have a little more respect for Yahoo, and know a little bit more about web hosting, (as well as what happens to your server when content goes viral).

fuckyeah

I also ended up talking to the people behind the Winnitron, the indie game machine, and as it turns out they are working on an exciting new project! I’m not at liberty to disclose the details, but it’s shaping up to be an impressive sequel to the popular cabinet. If you liked the Winnitron, you’ll love what they have planned next.

As usual, our next meeting will be on Tuesday at Seccuris, 321 McDermot Avenue. Updates on the space and voting on the wishlist will take place. Oh, and after seeing the raging success that was FuckYeahNouns, skullspace has decided to branch out into meme production, with the goal of 1 meme per month. If successful, we may sustain our business model through the propagation of viral internet content. Feel free to help us either with hosting space, idea donation, coding expertise and whatever else you think could spread like wildfire through the internet.

And some more pics from the meet:
people
table
console
Jay

The rest of the pictures can be found here

Monday, 7 March 2011

Code Camp - it's safe to say we won!

Greetings, Internet!

Winnipeg Codecamp for 2011 has come and gone. SkullSpace, with its own track, stickers, and a pile of free giveaways, managed to fill the 40-person room to capacity (and more!) all day. A number of members came out to support us, plus a bunch of people we don't know. We didn't see any other talks that day, but I think it's safe to assume that ours were the best!

Before I go on, a big thank you goes out to D'Arcy Lussier, Red River College, all the sponsors, and anybody else who helped make this happen!

The day started on a high note with Stef speaking on jQuery. Despite it being 9am on a Saturday morning, people were bringing in chairs from the other room. He gave a great overview of jQuery, complete with demos that included a jQuery-like library based on a story about the Unicode Snowman ("☃"). Download slides
IMG_6969

Introduction to jQuery from SkullSpace Winnipeg on Vimeo.


Next up was Mak's talk on the Nmap Security Scanner project. This talk did a brief overview of the Nmap project and the many different things it does (including the "arcane" OS-detection algorithms). Primarily, though, he covered covered the Nmap Scripting Engine, with discussions on how to write scripts for a variety of uses. Download slides
IMG_6975

Introduction to the Nmap Security Scanner from SkullSpace Winnipeg on Vimeo.


Lunch came next. Free food, as it turns out, was everybody's favourite part of the day.

After lunch, Ron (that's me!) spoke on stupid mistakes made by smart people. The talk covered a wide varitety of issues he's seen in the field, including protocol mistakes, bad crypto, poor use of randomization, and more. There were several demos, all of which, by some miracle, worked on the first try. Download slides
IMG_6985

Stupid Mistakes Made By Smart People from SkullSpace Winnipeg on Vimeo.


Next, Andrew impressed everybody with a talk on the spread of hackerspaces throughout Europe and North America. He concluded with an extended Q&A and discussion about SkullSpace. The audience had a lot of really great questions! Download slides
IMG_7019

Hackerspace Everywhere! Winnipeg: our time is now from SkullSpace Winnipeg on Vimeo.


And finally, Dan (who has a level 7 beard!) finished the day with a talk on theming Wordpress. After a bumpy start that he handled spectacularly, he walked the audience through developing a portfolio site featuring a picture of his un-bearded self. Unfortunately, we don't have any pictures of his talk (if you do have any, please share!).

We wrapped up the night by heading to the King's Head. After the other Code Camp folks went home, we joined up with a Reddit meetup and had a long, fun night! It's safe to say that everybody's favourite part was Andrew trying to find more Reddit people - everybody who came through the door was asked if they're from the Internet. Few were.

As a special treat to Codecamp guests (and you, now!) we had a special "secret challenge" that we hosted. The challenge, which is still playable, has been a rousing success with over two hundred players (two of whom have completed the challenge as a team and two of whom completed it themselves)!

Wednesday, 26 January 2011

Ron Bowes appreciation station

Welcome to Wednesday morning in our beautiful, sunny city! As promised, there'll be info on the Code Camp presentations, but before that we have another announcement.

Ron Bowes and SkullSpace have taken first place in the Nightmare Before Charlie Brown's Christmas hacker challenge, put on by The Ethical Hacker Network.

Imagine the situation: Ron, Mak, Andrew, and Russ huddled around computers in Ron's spare room, our half-broken hub humming away, threatening to die at any moment. We were trying to learn how VoIP, or voice over IP, could be hacked, guided by the contest writeup. The whiteboard was covered in hastily drawn diagrams, and our computers chugged along with a variety of new tools.

Little by little, we whittled away at the problem, figuring out how the contest scenario unfolded. Eventually, things started clicking into place, and we knew every detail about the problem! So we wrote up our submission and sent it in, fingers crossed. Today, the results finally came in - we took first place for the best technical answer! The prize (a book signed by Ed Skoudis himself) will be the first book in SkullSpace's library!

So, after having bested the competition, Ron will be giving back to the community with a talk on security and the mistakes people make.

The codecamp talk is called "Stupid Mistakes Made By Smart People" the talk will cover topics from "tricking SQL Server into arguing with itself to time servers amplifying denial of service attacks, useless encryption in ASP.net and PS3, and even an undisclosed loophole in a security camera that gives full access to anybody who tries." Winnipeg Code Camp takes place on Saturday, February 26. The exact time has yet to be announced, but we'll keep you updated and we hope to see you there!

For now, please enjoy these Japanese anatomical posters of godzilla-esque monsters:

http://www.pinktentacle.com/2011/01/illustrated-anatomy-of-gamera-and-foes/

Monday, 24 January 2011

moving parts, codecamp and you

We know it’s not even the end of the month yet, but we’ve already moved our calendars ahead and are staring intently at the last week few weeks of February. Not only are we still (constantly) stoked on the materialization of a physical space, but Red River College (and a bunch of generous sponsors) are putting on a free coding event!

http://winnipegcodecamp.com

Winnipeg Code Camp is going down Saturday February 26h, and it’s looking to be fairly awesome. Featuring local technology experts (including all three of our founding members) topics will range from coding, networking and security to physical hackerspaces. If that hasn't convinced you, keep in mind the event is at the amazing downtown campus, includes free breakfast and lunch ... and is a stone's throw from the King's Head.

Over the next few days we’ll go over the topics SkullSpace is involved in (and who’s covering them), but for now we'll leave you with this page of useful GIFs of various mechanisms:

http://www.core77.com/blog/object_culture/gifs_that_explain_basic_mechanisms_17220.asp

Wednesday, 19 January 2011

Cupcake Hackathon a success!

Last weekend, on Saturday, January 19th, SkullSpace hosted a cupcake hackathon as part of the Global Hackerspace Cupcake Challenge. There were 16 of us total who all made the long trip to Mak's place out on the edge of the world (well, Winnipeg). Of course, a hackerspace event wouldn't be proper without at least one major technical glitch. Since we had two, we knew it would be good! Our first setback was getting a decent wireless Internet connection in a house that, as far as we can tell, is made of lead. It took an hour and a hundred feet of cat5 cable, but that was solved. The second problem was ustream mysteriously failing under OS X, but rebooting into Windows fixed that. Once we had the infrastructure in place and ustream streaming, it began!

We ended up using a recipe for "french toast muffins," which are sweet, rich, and maple-y, just like Canadians! By law we had to call them cupcakes, and we didn't really know the difference, so we figured it's fine. Since we had two vegans (and three vegetarians!) at the event, we decided to make them entirely vegan, which was a great decision! For an extra touch of Canadian pride, we made a maple-flavoured icing to glaze them with. Our taste testing convinced us we made the right choice!

They were prepared:
IMG_0087

Baked:
IMG_0107

Glazed:
IMG_0106

Topped with powdered sugar and cinnamon:
IMG_0113

And, finally, shipped:
IMG_0115

In the end, we shipped a whole dozen (complete with the pan they were baked in!) over to BuildBrighton in Brighton, England, a 6500km (and $80) journey. We hope they get there safe and sound! We also sent one to Black Lodge Research in Redmond, WA, USA, and one member took it upon himself to send two more cupcakes (that he assures me he didn't just eat!) to a boss/friend in Puerto Rico and to a friend in Madison, Wisconsin.

Aside from baking cupcakes we had some other projects going on. Several members brought their lockpicking sets and a plethora of locks so we set up a little "lockpicking village" (which, as it turns out, is a table with locks on it) in the basement. Since it was the first time picking locks for many, it was an exciting experience (and gave us a great idea for one of our first workshops!). Of course, as always, we emphasized the legal and ethical aspects of lockpicking, just like any other security activity.
IMG_0098
IMG_0094
IMG_0102
IMG_0104

And here's what it looks like when everybody photobombs the same picture:
IMG_0095

At another table upstairs we had 4-5 people doing some software development, working on a secret project (of course, since it's on our SkullSpace github account, it isn't very secret). Hopefully in the next couple months, we'll have an actual release!

Since nobody got a picture of the coding, here's Mak in a hat:
IMG_0117

Dave hugging Andrew the Greater:
IMG_0089

And the winner of the Best Hat contest:
IMG_0092

At the end of the day we had almost 3 hours of video footage from the ustream account. Unfortunately this was very very low quality - 320x240 at 11fps. We took some small clips from that footage and made a little trailer video for the event, which you can view on youtube. We plan to edit up the raw footage and release a longer highlights video with sound in the near future. We also put together a dance number [WARNING: audio] that I don't recommend watching.

Another great thing that happened on Saturday was the pile of donations we received! We had mentioned previously that donations were being accepted, but that it was completely optional, and just people showing up was enough. We tried doing the hard sell, timeshare style, and locked the door. But, since we had muffins and computers nobody seemed to mind. So we tried Plan B and simply asked people to chip in and ended up raising an unbelievable $249! This was much, much more than we ever expected and we are grateful to everyone who donated. This money will help pay off our debts to dangerous loansharks (okay, that's not true) that we already accrued by filing the articles of incorporation, the costs of registering the domain name, postage to England, and, of course, the 70 cent envelope and stamp we had to buy.

We've emphasized this in our meetings and events, but we want to emphasize it again: none of the money we're receiving through SkullSpace, not now or any time in the future, is paid to employees/administrators/members. We are, and always will be, run strictly by volunteers (in fact, even we put money in). This means any and all work people do on behalf of SkullSpace is on a volunteer basis, and any money we take in goes directly towards the benefit of all the members and the space itself, rather than any one member/director/king/etc. We feel this is important as the goal here is not financial gain, but to create a solid community of like-minded people.

So, that brings our first big event to a close, and we all had a great time! I can't wait to see what the future holds for SkullSpace, and hopefully we'll see you there!

If you haven't already, please subscribe to our mailing list, follow us on twitter, like us on Facebook, comment on our youtube videos, and, of course, gaze in wonder at our Flickr pictures!